Top Software Composition Analysis Tools for Compliance

If your application uses open-source code, it means that you are relying on components you didn’t write and can’t fully control, including the vulnerabilities coming with that code.
This is where you should consider using Software Composition Analysis (SCA) tools, which scan your dependencies and catch any hidden security issues or risky licenses before they cause problems.
Below, we will offer some of the top Software Composition Analysis Tools that you can consider for your development workflows. And before we start reviewing them one by one, here is a quick comparison table with features and pricing info included.
Features | Pricing | Best for | |
| Aikido Security |
|
| Individual developers, startups, and growing teams |
| Snyk |
|
| Individual developers and development teams |
| Socket Security |
|
| Individual developers and growing teams |
| Checkmarx |
| Custom quote | Developers and AppSec teams |
1. Aikido Security
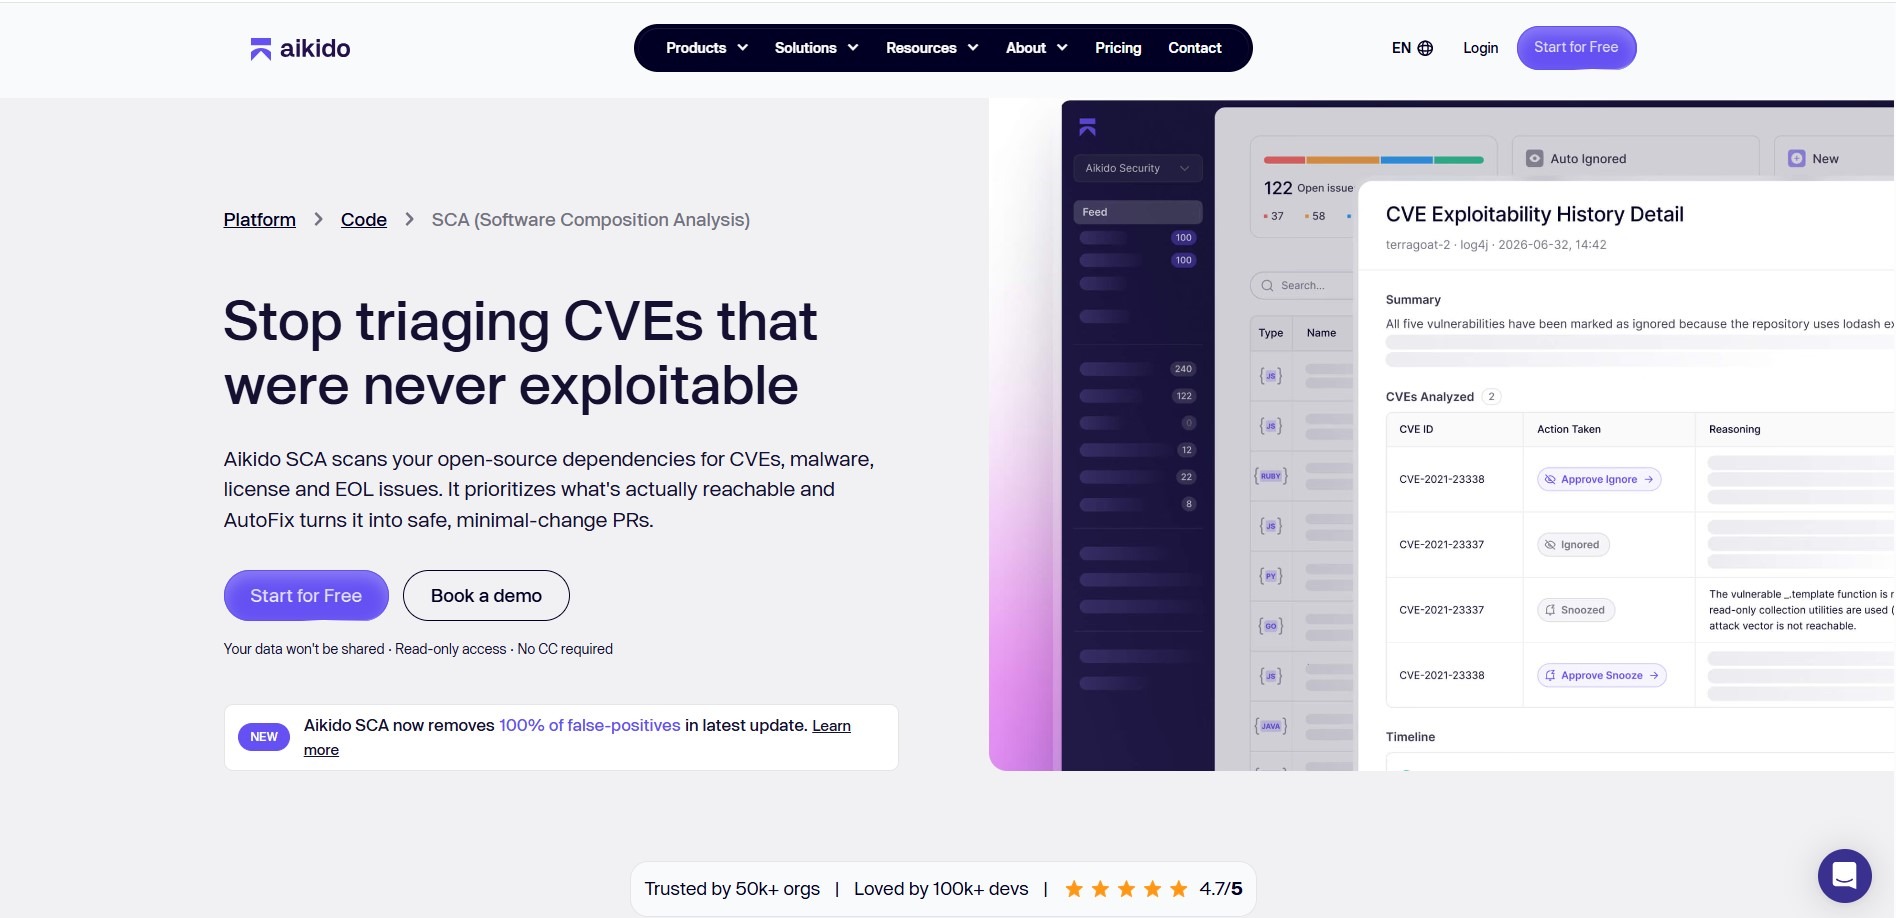
Aikido Security is a unified security platform that also provides software composition analysis solutions. It works by scanning your open source code dependencies and identifying any common vulnerabilities and exposures (CVEs). It also flags malware, license, and EOL issues, so you can fix them before they cause security or legal issues.
It stands out among other SCA tools for its reachability analysis, where instead of simply reporting a vulnerability, it traces whether your code actually calls the vulnerable part of that library.
Key features
- Reachability + Exploitation analysis
- Full software visibility with SBOMs
- SCA integrated across your entire SDLC
- Vulnerability protection with Aikido Intel
Pricing
- Standard Pentest: The pricing starts at $4000 per assessment
- Aikido Platform: Starts at $350/month (up to 10 users). A free plan is also available for up to 2 users.
Best for: Individual developers, startups and growing teams
2. Snyk
Snyk Open Source is a security management tool that helps developers find, prioritize, and fix open source security vulnerabilities and license issues. You can find vulnerabilities while coding in your IDE or CLI, add security guardrails to your CI/CD pipelines, and test your production environment for existing vulnerabilities.
Key features
- Remediation prioritization based on the risk level
- Fast fixing to reduce exposure
- Continuous monitoring
- Open source management automation
Pricing
Individual developers can start with Snyk for free, while bigger teams can subscribe to the pricing plans offering more functionality, starting at $25/month per contributing developer.
Best for: Individual developers and development teams
3. Socket Security
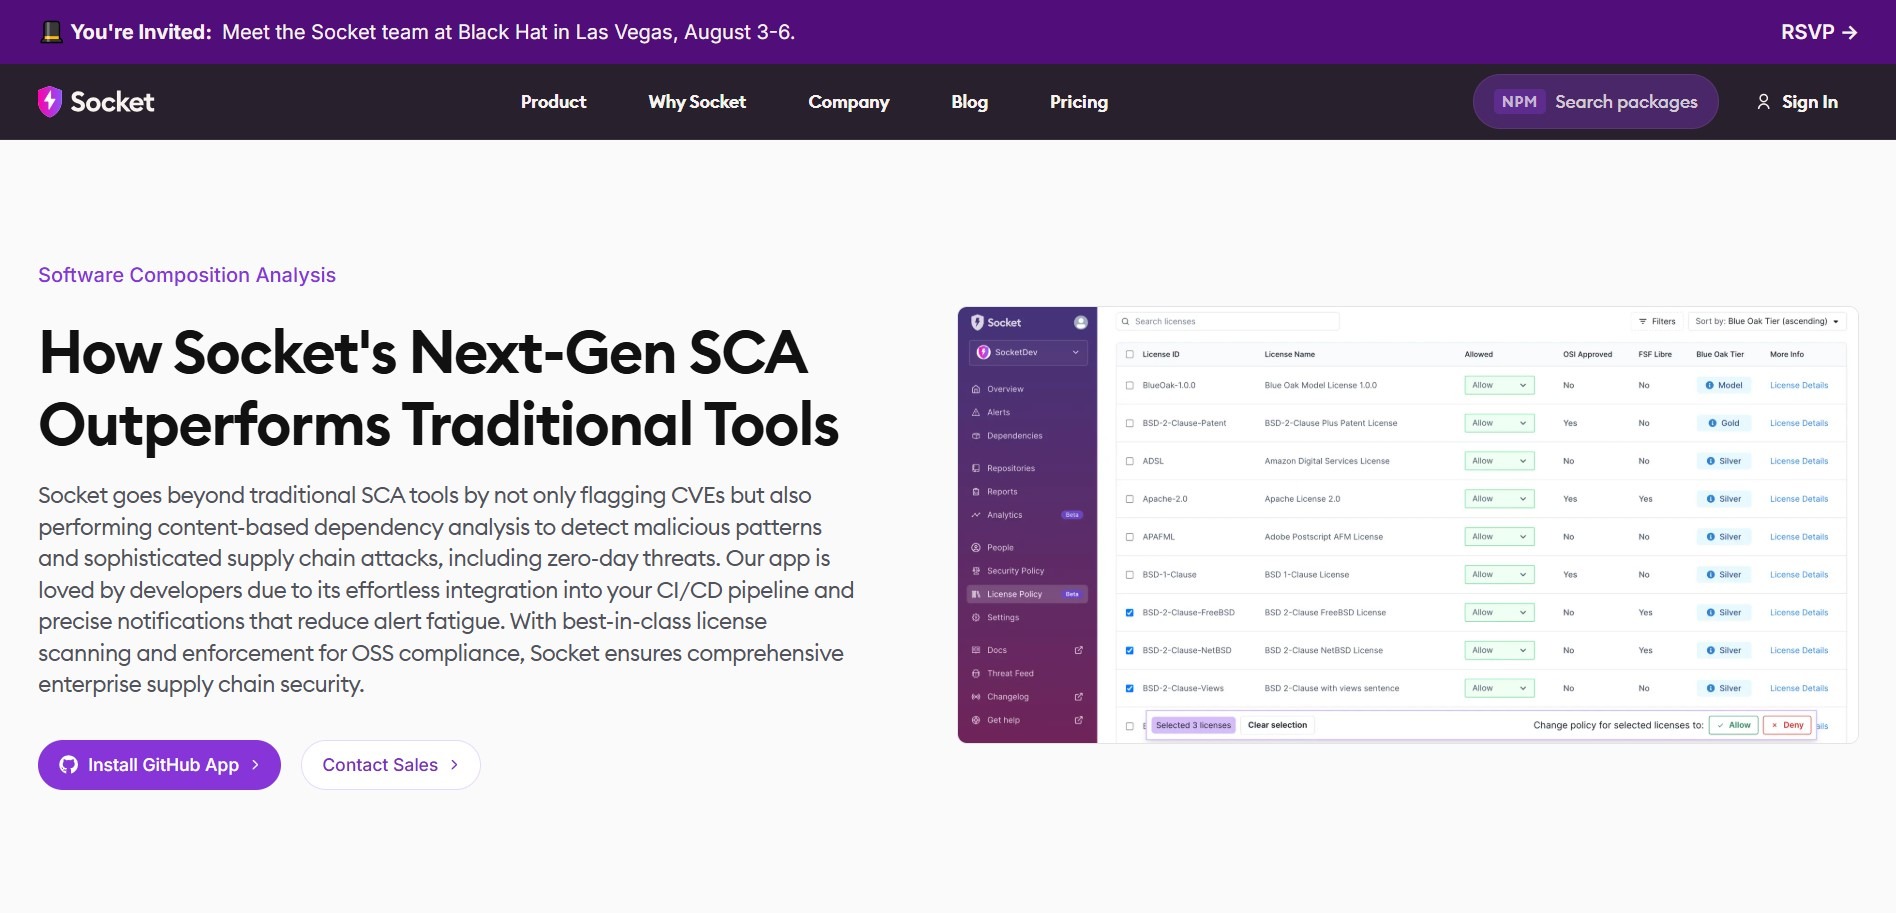
Socket Security’s SCA solutions scan open source dependencies for both known vulnerabilities (CVEs) and suspicious code behavior, catching malicious packages and zero-day supply chain attacks. It easily integrates into CI/CD pipelines and also scans and enforces open source license policies, helping teams stay compliant while protecting against a broader range of supply chain threats.
Key features
- Protection against zero-day supply chain attacks
- Vulnerability scanning (CVE's)
- Open source dependency visibility
- Dependency optimization tools
- Best-in-class open source license scanner
- Configurable license enforcement policy
- Integrations for all your favorite tools
Pricing
Socket Security also offers a free plan for individual developers to test its features. The paid plans start at $25 /per month /per developer.
Best for: Individual developers and growing teams
4. Checkmax
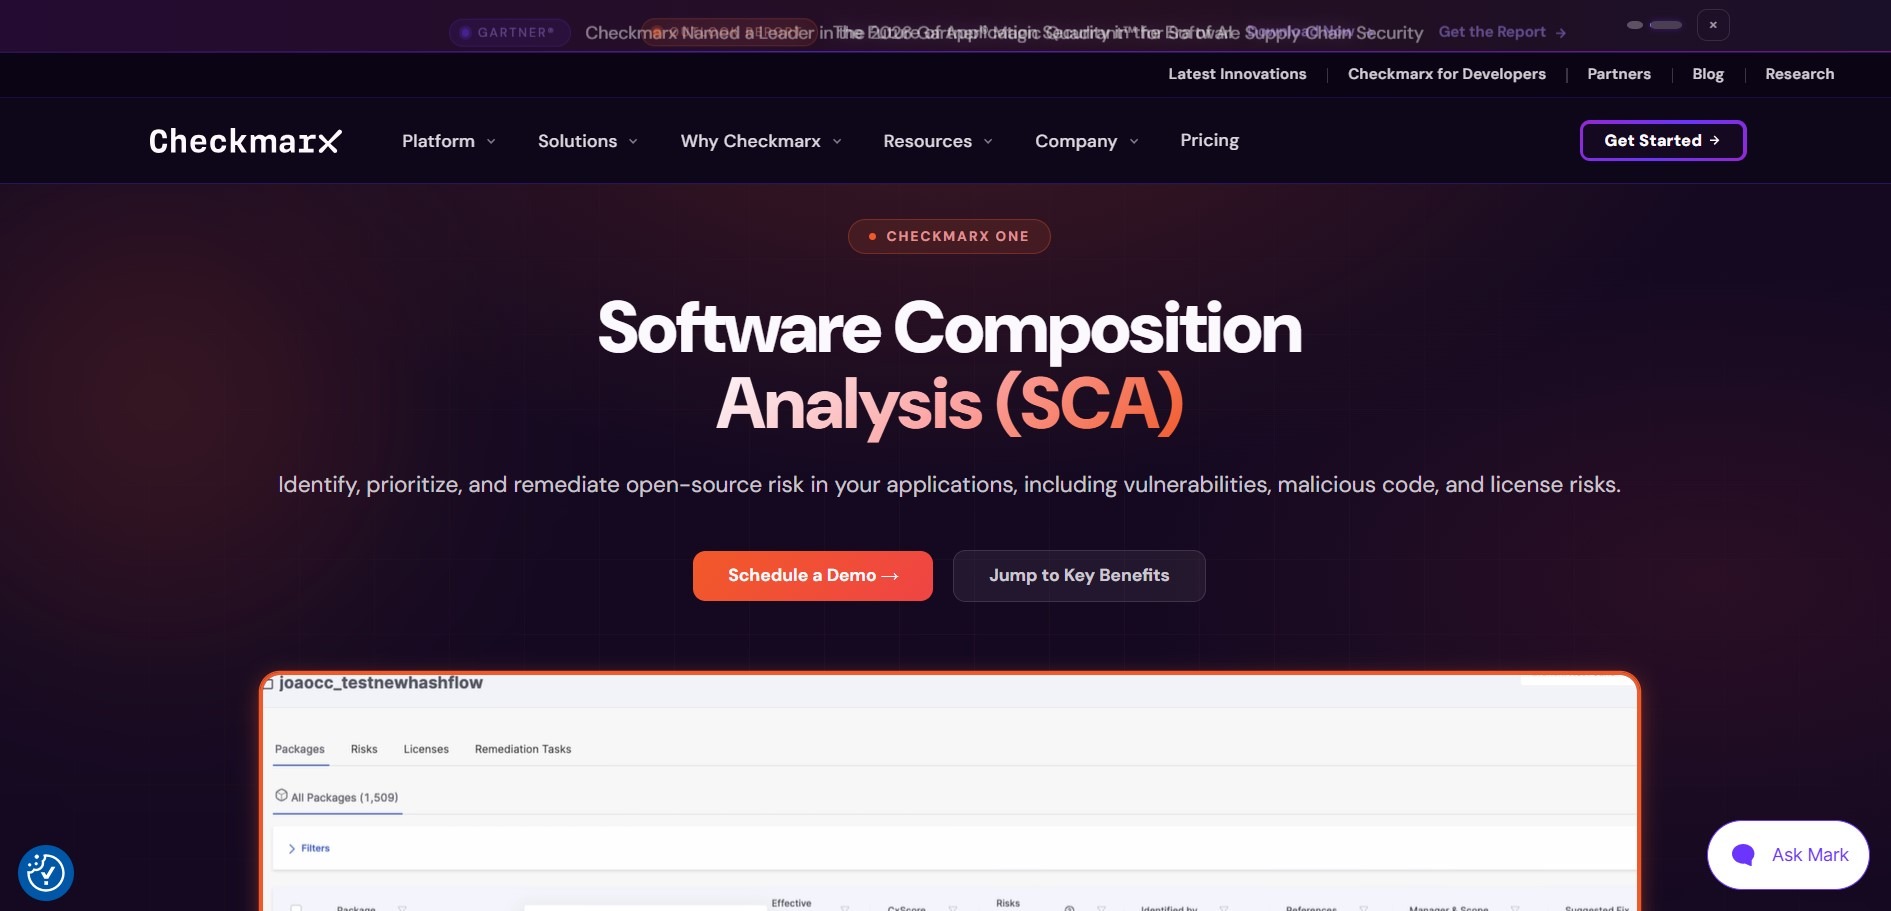
Checkmarx SCA scans your open source dependencies to find vulnerabilities, malicious packages, and license risks. It uses reachability analysis to prioritize only the issues that could actually be triggered in your running app. It integrates into your IDE, CLI, and CI/CD tools and gives prioritized remediation guidance for fixing what matters most.
Key features
- SCA scan accuracy
- Deep dependency scanning
- Malicious package protection
- Reachability analysis
- Actionable remediation guidance
- Policy automation
- License risk management
- SBOM
Pricing
Checkmarx offers a custom quote based on the models that match your attack surface.
Best for: Developers and AppSec teams
So, What is the Final Pick?
Open source code is a fast move in software development, but they also come with vulnerability and license risks. Modern SCA tools help you address these issues and fix them before it is too late.
By doing so, choose Aikido Security for its advanced reachability analysis, Snyk for remediation prioritization features, Socket Security for scanning existing and potential vulnerabilities, and Checkmarx for SBOM generation and management.
Related Blogs

What is VPN Proxy Masterand and what makes it the top choice for many users today? It is a tool that supports secure internet access, allows overcoming geographical barriers and protects personal data from cyber threats. In this article, Antidetect Browser Hidemium will provide detailed information about VPN Proxy Master, including the Main features, benefit, as well as How to install and use[…]
In 2025, making 100 dollars online per day has become more realistic than ever. The rapid development of digital platforms and new business models has created opportunities for anyone to build a stable source of income right at home. In this article, Hidemium will introduce 21 legal methods that help you increase your profits, along with helpful tips to maximize your earning potential.1.[…]
When managing multiple accounts for MMO, eCommerce, or multi-platform marketing, IP address and geographic location are always among the top risk factors. If multiple accounts log in from the same IP or an incorrect location, platforms can easily detect account linkage, leading to suspensions or bans.This is also why using a proxy alone is no longer sufficiently safe. A more sustainable solution[…]
.png)
In the online business and social network management environment, using multiple accounts on the same platform such as Facebook, Twitter or Amazon is a common need. Ghost Browser was born as a convenient solution, helping users easily manage multiple accounts in a single browser interface. This article Hidemium will explain what Ghost Browser is, why it has become the favorite choice of many[…]
A bug that appears on one tester's machine but disappears on another is one of the most frustrating problems in QA.The same website may behave differently depending on:whether the user is logged in;which cookies already exist;local storage;browser settings;proxy location;previous sessions;account state;device or browser environment.That means QA is often not just about testing a page.It is about[…]
Best Octo Browser Alternative in 2026: Hidemium vs Octo Browser for Growing TeamsThe best Octo Browser alternative in 2026 is Hidemium for growing teams that need browser profiles, proxies, workspaces, team access, and scalable account operations. In the Hidemium vs Octo Browser comparison, Octo Browser is strong for polished profile control, while Hidemium is stronger for teams that need[…]